Revision poster: workload identity and hardening.
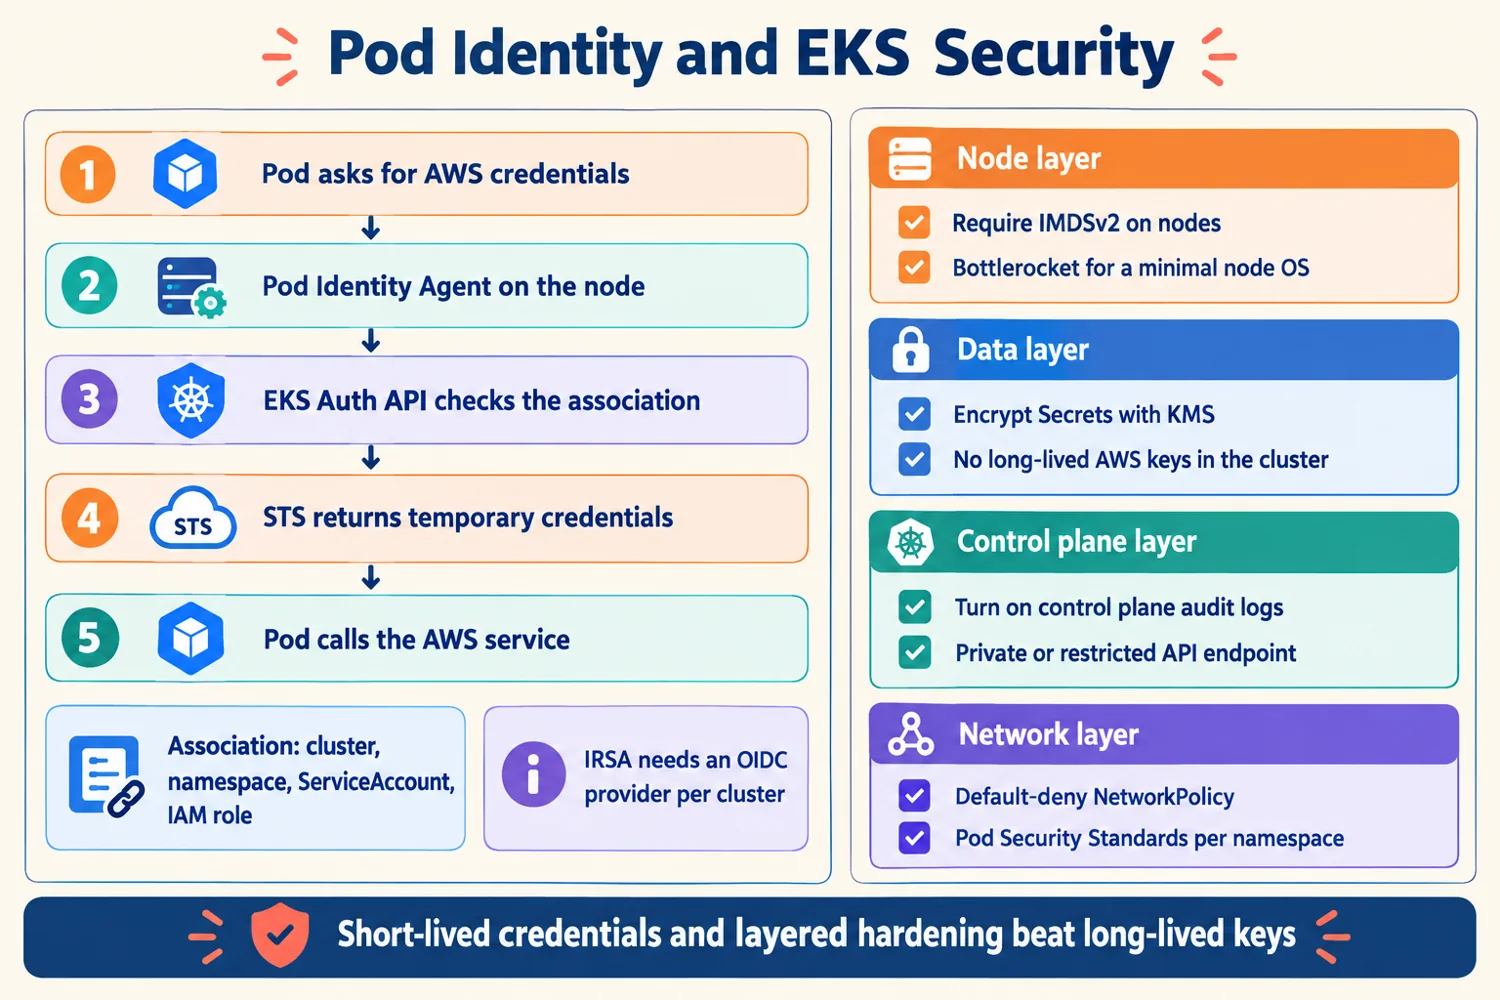
Left: how a Pod gets short-lived AWS credentials. Right: the hardening checklist grouped by layer.
- 1Pods get temporary credentials via the Pod Identity Agent and STS, scoped to the associated role.
- 2An association links cluster, namespace and ServiceAccount to an IAM role.
- 3IRSA needs an OIDC provider per cluster; Pod Identity does not.
- 4Require IMDSv2 and use a minimal node OS.
- 5Encrypt Secrets with KMS and keep no long-lived AWS keys in the cluster.
- 6Enable audit logs, restrict the endpoint, default-deny network policy and Pod Security Standards.
Self-check: cover the poster and answer
- Why is the Pod Identity trust policy reusable across clusters?
- Which control stops a Pod stealing the node role through metadata?
Short-lived credentials and layered hardening beat long-lived keys.