Revision poster: access, endpoint and version lifecycle.
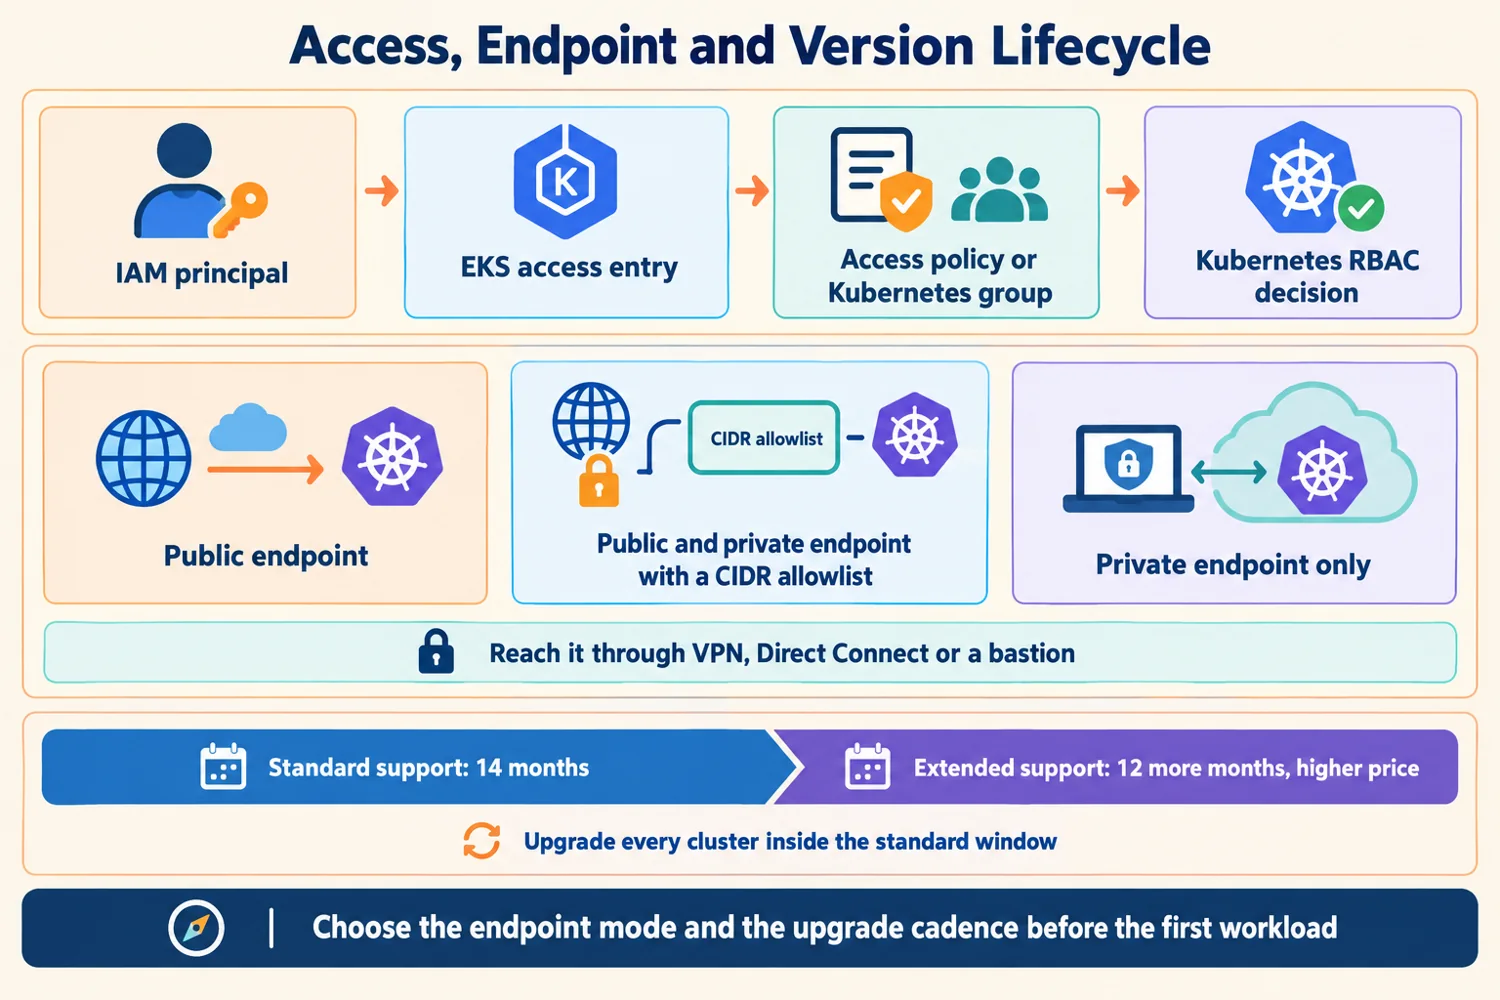
Top: how an IAM identity becomes Kubernetes permissions. Middle: the three endpoint modes. Bottom: the version support timeline.
- 1An IAM principal gets an EKS access entry, which carries access policies or Kubernetes groups.
- 2RBAC makes the final authorization decision inside the cluster.
- 3Public only is exposed, public plus private with an allowlist is the common production choice, private only is the tightest.
- 4Standard support lasts about 14 months, extended support 12 more at a higher price.
- 5Decide the endpoint mode and upgrade cadence before the first workload.
Self-check: cover the poster and answer
- Why are access entries safer than the aws-auth ConfigMap?
- Which endpoint mode needs VPC endpoints for ECR and STS?
Choose the endpoint mode and the upgrade cadence before the first workload.