Revision poster: Pod IPs, Services, DNS, policy and ingress.
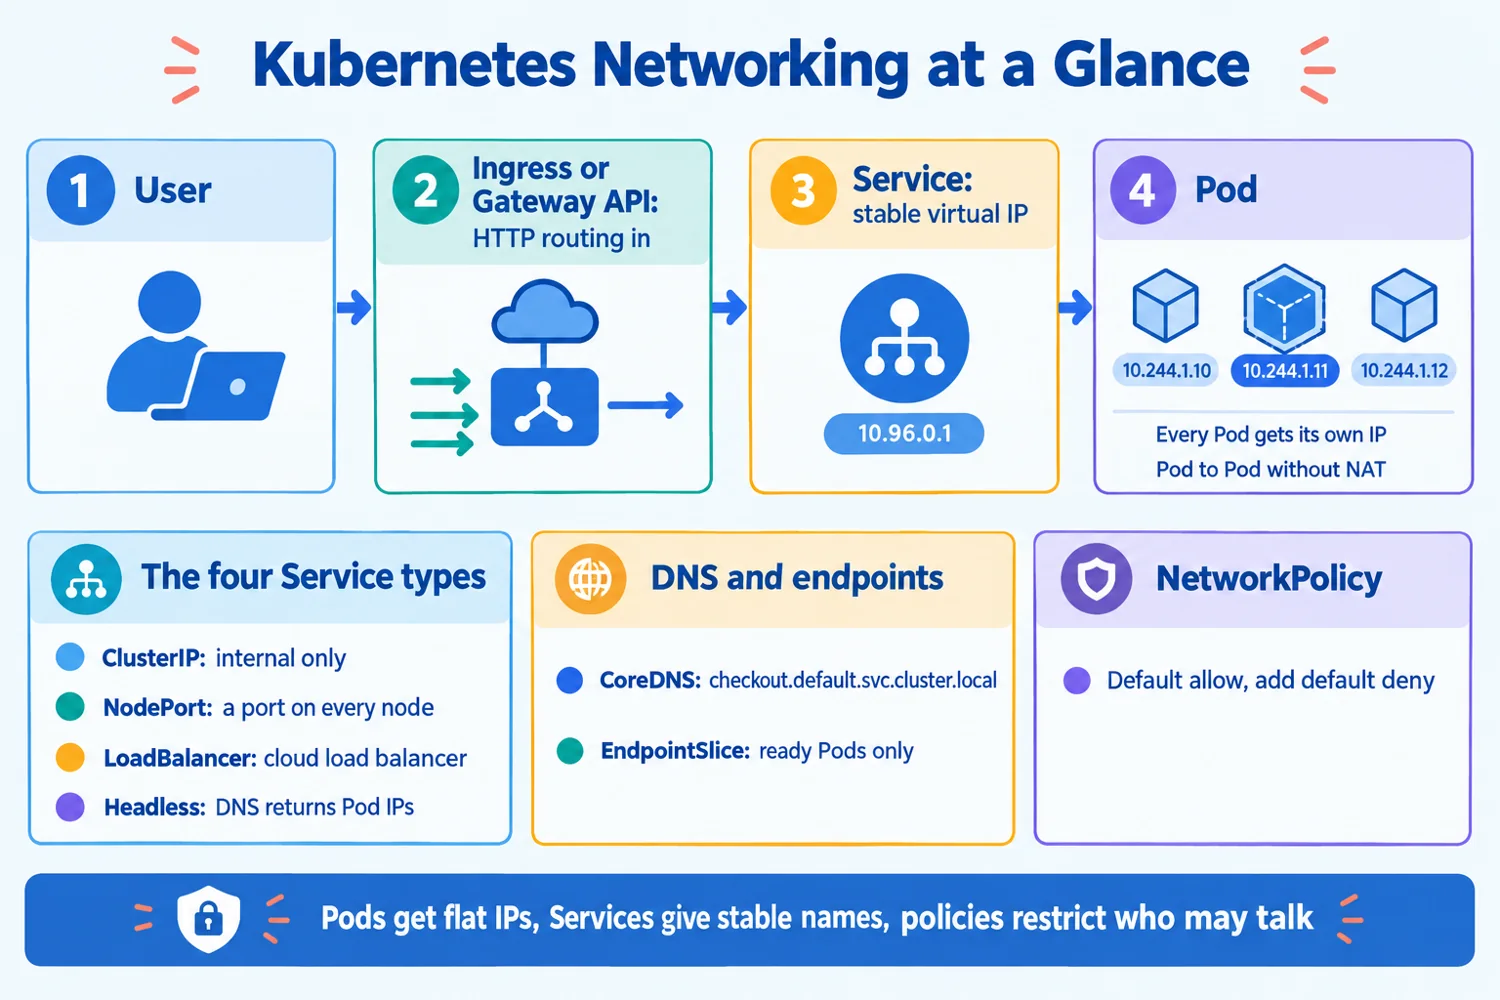
The top row is the traffic path. The bottom row groups the supporting mechanisms.
- 1Every Pod has its own IP and reaches other Pods without NAT.
- 2A Service gives a stable virtual IP and name over changing Pods.
- 3ClusterIP is internal, NodePort opens a port on every node, LoadBalancer asks the cloud, ExternalName is an alias.
- 4CoreDNS resolves names; EndpointSlices list ready Pods only.
- 5NetworkPolicy starts open: add default deny, then explicit allows.
- 6Ingress or Gateway API routes HTTP from outside.
Self-check: cover the poster and answer
- A Service exists but traffic gets a 503: what do you check first?
- Why does a NetworkPolicy sometimes do nothing at all?
Pods get flat IPs, Services give stable names, policies restrict who may talk.